TECH
eMudhra Security Alert: Government Forms Special Investigation Team After Certificate Vulnerability Raises Cybersecurity Concerns
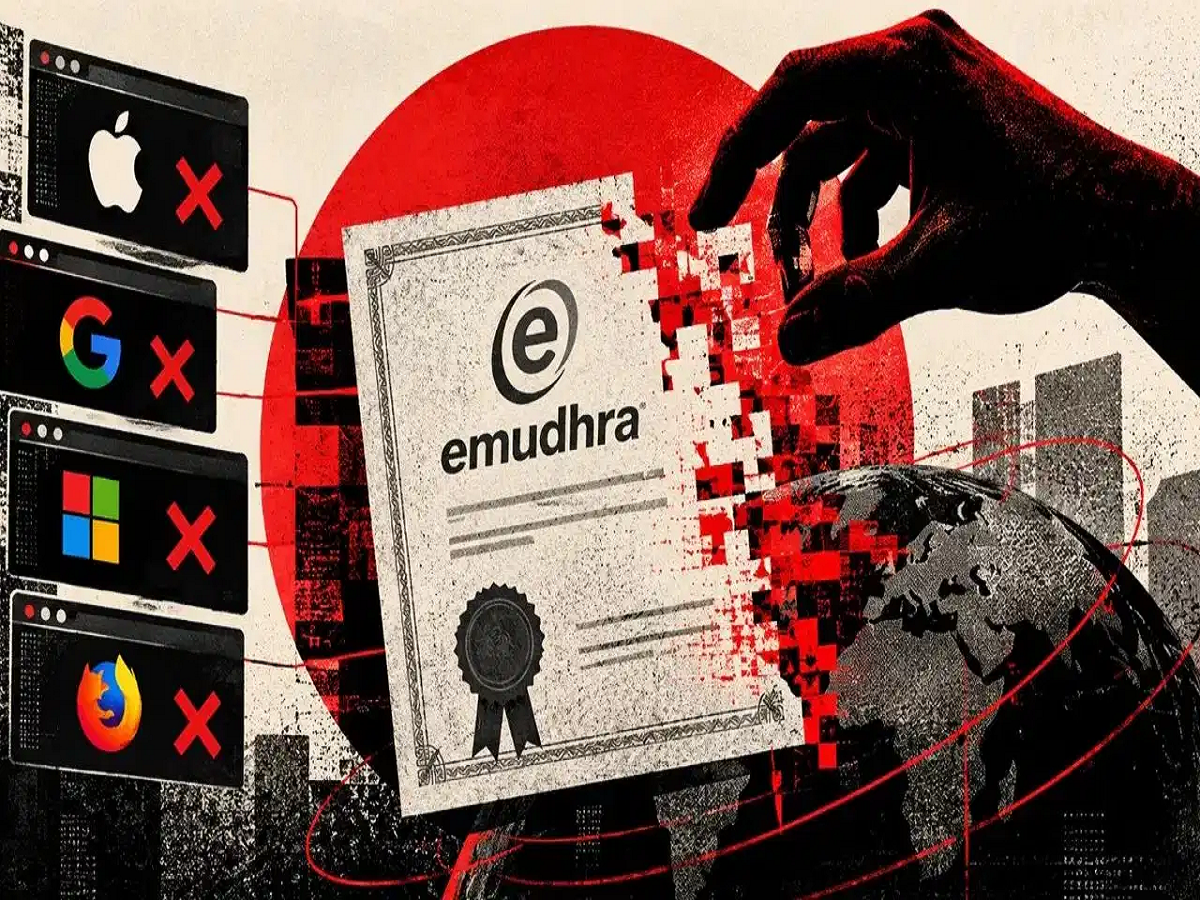
The Indian government has stepped up its response to a reported cybersecurity incident involving eMudhra, a company that provides digital certificate and authentication services. The Ministry of Electronics and Information Technology (MeitY) has taken note of the issue and constituted a special team to investigate the matter.
According to the ministry's statement, the incident had a limited and short-lived impact on Indian websites and applications. The government has also sought to address public concerns about the safety of digital services, clarifying that eMudhra's regulated Digital Signature Certificate (DSC) and eSign services were not affected by the reported incident.
The case highlights the importance of digital certificate security, particularly as banking, government services, online transactions, and business communications increasingly depend on trusted digital identities.
1. What Is eMudhra and Why Is It Important?
eMudhra is an Indian digital trust service provider that offers Digital Signature Certificates, electronic signature services, and digital certificates used to secure online communications.
Its services support a variety of activities, including digitally signing documents, completing electronic transactions, and establishing secure connections between websites and users.
Digital certificates play an important role in online security. They help browsers verify a website's identity and establish encrypted connections, reducing the risk of sensitive information being intercepted during transmission.
However, different types of digital certificates serve different purposes. Certificates used to secure website connections are not the same as those used for digitally signing documents. Understanding this distinction is essential when assessing the impact of a cybersecurity incident.
2. What Happened in the eMudhra Security Incident?
The reported incident concerns eMudhra's Public Key Infrastructure (PKI), the system used to create, manage, and validate digital certificates.
According to the information provided, a technical weakness was identified in private keys associated with eight intermediate certificates created on April 30, 2025.
Private keys are sensitive cryptographic components used to establish digital trust. If a private key is weak, exposed, or predictable, an attacker may be able to exploit it to undermine the security provided by the associated certificate.
The reported vulnerability raised concerns about whether malicious actors could potentially misuse affected certificates. The matter attracted attention from cybersecurity researchers and technology companies, prompting further investigation and mitigation efforts.
The exact technical scope and consequences of the incident must be established through the ongoing investigation rather than assumed from the initial reports.
3. How Could a Weak Digital Certificate Put Users at Risk?
To understand the potential danger, consider what happens when you visit a banking website or another secure online service.
Your browser checks the website's digital certificate to help verify its identity. The certificate works alongside cryptographic keys and other security mechanisms to establish trust.
If an attacker can exploit a compromised or vulnerable certificate authority chain, they may potentially attempt to create fraudulent certificates or impersonate legitimate websites under certain conditions.
This could expose users to phishing attacks, fake websites, or attempts to intercept sensitive information, including login credentials.
However, a certificate vulnerability does not automatically mean that every website associated with a provider has been compromised. The actual risk depends on which certificates and keys were affected, whether they could be exploited, and what protective measures were implemented.
Users should therefore distinguish between a reported security weakness and confirmed evidence of data theft or widespread website compromise.
4. How Was the Vulnerability Reportedly Discovered?
According to the supplied report, an independent security researcher identified the weakness while examining the relevant cryptographic keys. Artificial intelligence tools were reportedly used as part of the research process.
The issue was subsequently brought to the attention of major technology companies, including Apple, Google, Microsoft, and Mozilla.
Browser and operating-system vendors play an important role in digital certificate security because they maintain trust systems that determine which certificate authorities are recognised by their products.
When a certificate authority's security is questioned, affected parties may need to assess the risk, investigate the underlying cause, and take appropriate measures. Depending on the findings, these measures can include revoking certificates, replacing keys, updating trust configurations, and notifying affected organisations.
The precise remediation steps and their completion status should be confirmed through official technical advisories.
5. What Has the Indian Government Said?
MeitY has stated that it has taken the reported incident seriously and formed a special team to investigate it.
The ministry also indicated that the impact on Indian websites and applications was limited and short-lived. Relevant stakeholders are working to address the issue, while the Indian Computer Emergency Response Team (CERT-In) has issued a security advisory outlining mitigation measures.
The government has further clarified that eMudhra's regulated Digital Signature Certificate and eSign services were unaffected by the incident described in its statement.
This distinction is important because the security incident concerns a particular part of the company's digital certificate infrastructure, rather than necessarily affecting every service it provides.
Authorities have also cautioned against relying on unverified claims circulating on social media. Further details are expected to depend on the findings of the investigation.
6. What Should Internet Users Do to Stay Safe?
Although the government has described the impact as limited, following basic cybersecurity practices remains important.
Verify website addresses: Check the domain name carefully before entering passwords or financial information. A padlock symbol alone does not guarantee that a website is legitimate.
Avoid suspicious links: Do not open unexpected links or attachments in emails, text messages, or social media posts, especially those requesting account details.
Keep software updated: Install browser, operating-system, and security updates when they become available. These updates can include important certificate and security protections.
Use multifactor authentication: Where available, enable an additional authentication method to make it harder for someone to access your account using only a stolen password.
Follow official advisories: If you operate a website or manage an organisation's IT systems, consult CERT-In guidance and the relevant service provider's technical notices for instructions specific to affected certificates.
There is no need to assume that personal information has been stolen solely because a certificate vulnerability has been reported. Any action should be guided by confirmed information and relevant security advice.
The Bottom Line
The eMudhra incident highlights how weaknesses in digital certificate infrastructure can raise broader questions about online trust and cybersecurity. MeitY has formed a special investigation team, and CERT-In has issued guidance intended to help mitigate potential risks.
The government has stated that the impact on Indian websites and applications was limited and short-lived, while the regulated DSC and eSign services were not affected by the reported incident.
The investigation's findings will be important in determining the precise scope of the vulnerability and whether further action is required. In the meantime, users and organisations should follow official advisories, maintain updated software, and continue practising safe online habits.